# IPv6 DHCPv6 Guard
**URL:** https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705
**Category:** Lessons Discussion
**Created:** [April 26, 2018, 10:50am UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705 "2018-04-26T10:50:56Z")
**Posts on this page:** 13
**Page:** 1
### Author:  [@ReneMolenaar](https://forum.networklessons.com/u/ReneMolenaar)
#### Post date: [April 26, 2018, 10:50am UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/1 "2018-04-26T10:50:56Z")
This topic is to discuss the following lesson:
> **[IPv6 DHCPv6 Guard](https://networklessons.com/cisco/ccie-routing-switching-written/ipv6-dhcpv6-guard)**
>
> IPv6 DHCPv6 Guard is one of the FHS (First Hop Security) mechanisms which inspects DHCPv6 messages between a client and server.
---
### Author:  [@nitayp1](https://forum.networklessons.com/u/nitayp1)
#### Post date: [November 13, 2019, 9:09am UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/2 "2019-11-13T09:09:39Z")
Hi Rene,
Does the DHCPv6 GUARD feature also builds a binding table to be used with IPV6 Source Guard?
Thanks in advanced.
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [November 13, 2019, 12:19pm UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/3 "2019-11-13T12:19:34Z")
Hello Nitay
The binding table is built by the DHCPv6 feature itself. The DHCPv6 Guard feature prevents the binding table from registering DHCPv6 replies and advertisements from rogue DHCPv6 servers. So DHCPv6 Guard protects the binding table from being populated by an non-endorsed source.
This protected binding table is then used by IPv6 Source Guard to filter inbound traffic on L2 switch ports that are not in the IPv6 binding table. More info on the IPv6 Source Guard feature can be found at the following link.
> **[IPv6 Source Guard](https://networklessons.com/ipv6/ipv6-source-guard)**
>
> IPv6 source guard is a switch feature that checks the source of IPv6 packets and checks if the source is in the IPv6 binding table.
I hope this has been helpful!
Laz
---
### Author:  [@nitayp1](https://forum.networklessons.com/u/nitayp1)
#### Post date: [November 13, 2019, 12:42pm UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/4 "2019-11-13T12:42:51Z")
Hi Laz,
Thanks for your reply.
Does the DHCPv6 Feature is an built-in Feature on every IPv6 capable switch,and the DHCPv6 Feature works just like dhcpv4 snooping when configured statically on a switch with the command `ip dhcp snooping`?
Thanks again very much, I appreciate your time!
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [November 13, 2019, 3:53pm UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/5 "2019-11-13T15:53:52Z")
Hello Nitay
DHCP Snooping uses a little bit of a different philosophy compared to IPv6 DHCPv6 Guard. Where DHCP snooping configures trusted and untrusted ports, IPv6 DHCP Guard is capable of creating client or server policies per port, is able to filter based on specific prefixes, and can also take advantage of preference filtering as stated in the lesson. IPv6 DHCP Guard does not create a table that is similar to the DHCP snooping table.
I hope this has been helpful!
Laz
---
### Author:  [@nitayp1](https://forum.networklessons.com/u/nitayp1)
#### Post date: [November 13, 2019, 4:14pm UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/6 "2019-11-13T16:14:59Z")
Thanks Laz,
You mentioned the “DHCPv6 Feature” as a whole different feature compared to the “DHCPv6 Guard Feature”, and you mentioned that the first one is building the binding table.
I understand that the DHCPv6 Guard is used exactly like port-security which you must configure it on each and every port that should be connected to an end device, otherwise an attacker could spoof DHCPv6 messages.
I also learned that you have IPV6 snooping Feature in the IPv6 Source Guard Lesson but again - you mentioned that “DHCPv6 Feature” and now I wonder if you meant DHCPv6 Guard Feature or if there is actually a DHCPv6 Feature which is default on IPv6 capable switches that builds the binding table using some kind of snoop9ing method?
Thanks you very much!
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [November 14, 2019, 6:26am UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/7 "2019-11-14T06:26:39Z")
Hello Nitay
> [@nitayp1](#):
>
> You mentioned the “DHCPv6 Feature” as a whole different feature compared to the “DHCPv6 Guard Feature”, and you mentioned that the first one is building the binding table.
Sorry, about the terminology, let me clarify. When I said the DHCPv6 Feature, I simply meant DHCPv6. It is DHCPv6 that builds the binding table, the same type of binding table that DHCP builds for IPv4. IPv6 DHCPv6 Guard and IPv6 Source Guard are two additional mechanisms that both involve the DHCPv6 service.
I hope this clarifies things…
Laz
---
### Author:  [@nitayp1](https://forum.networklessons.com/u/nitayp1)
#### Post date: [November 14, 2019, 8:10am UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/8 "2019-11-14T08:10:03Z")
Thanks Laz,
Then I would like to know if the DHCPv6 builds the binding table automatically or not? because the DHCPv4 Feature only builds the binding table on a switch after implementing DHCP snooping, so what I’m asking is that: would DHCPv6 doesn’t necessary needs any feature on an IPv6 capable switch to enable the creation of a binding table while for IPv4 the witch must have being configured with the DHCP snooping feature?
Thanks you very much.
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [November 15, 2019, 6:25am UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/9 "2019-11-15T06:25:54Z")
Hello Nitay
> [@nitayp1](#):
>
> …because the DHCPv4 Feature only builds the binding table on a switch after implementing DHCP snooping,
In IPv4, DHCP always builds the binding table, without the use of DHCP snooping. When you enable DHCP snooping, it will build the **DHCP snooping binding table**. These are two different tables. The first is used by DHCP to simply list the IP address leases that have been given out to particular hosts. You can view this table using the `show ip dhcp binding` command like so:
```
Router#show ip dhcp binding
Bindings from all pools not associated with VRF:
IP address Client-ID/ Lease expiration Type
Hardware address/
User name
10.16.173.0 24d9.2141.0ddd Jan 12 2013 03:42 AM Automatic
10.16.173.18 24d9.214a.6dd3 Jan 12 2013 04:59 AM Automatic
10.16.173.21 24d9.214a.eee9 Jan 12 2013 03:49 AM Automatic
10.16.173.24 24d9.214a.13d6 Jan 12 2013 03:12 AM Automatic
```
This table includes IP lease, the corresponding MAC address of the host, the lease expiration and the type.
Now the DHCP snooping binding table is different. This table keeps track of DHCP addresses and includes information such as VLAN number and interface information. The important thing here is the interface info maintained by the table. Information on this table can be seen using several commands such as:
```
SW1#show ip dhcp snooping
<--output ommitted -->
Interface Trusted Rate limit (pps)
------------------------ ------- ----------------
FastEthernet0/1 no 10
FastEthernet0/2 yes unlimited
```
and…
```
SW1#show ip dhcp snooping binding
MacAddress IpAddress Lease(sec) Type VLAN Interface
------------------ --------------- ---------- ------------- ---- --------------------
00:0C:29:28:5C:6C 192.168.1.1 85655 dhcp-snooping 1 FastEthernet0/1
```
I know I went into a lot of detail, but I just want to be clear. Now when it comes to IPv6, DHCPv6 creates a binding table that corresponds IPv6 addresses to MAC addresses just like DHCP does. This is a fundamental part of how DHCPv6 works. But, DHCPv6 Guard, unlike DHCP snooping, does not build a DHCP snooping binding table.
I hope this has been helpful!
Laz
---
### Author:  [@jgarayarq](https://forum.networklessons.com/u/jgarayarq)
#### Post date: [February 10, 2023, 5:23am UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/10 "2023-02-10T05:23:54Z")
Hello, what version of IOS do I have to use to be able to implement this feature in GNS3? It happens that I don’t get all the commands. What do you recommend.
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [February 12, 2023, 6:53am UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/11 "2023-02-12T06:53:58Z")
Hello José
According to this [Cisco command reference](https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/ipv6/command/ipv6-cr-book/ipv6-i1.html#wp2417516200), the DHCPv6 guard feature was introduced in Cisco IOS version 15.2(4)S. In GNS3 it also depends upon what type of IOS you are using. Can you share with us your IOS version? Also, can you specify which commands are not available in your particular version so we can help you out further?
I hope this has been helpful!
Laz
---
### Author:  [@jgarayarq](https://forum.networklessons.com/u/jgarayarq)
#### Post date: [February 12, 2023, 10:55pm UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/12 "2023-02-12T22:55:01Z")
Hello, this is my IOS version:
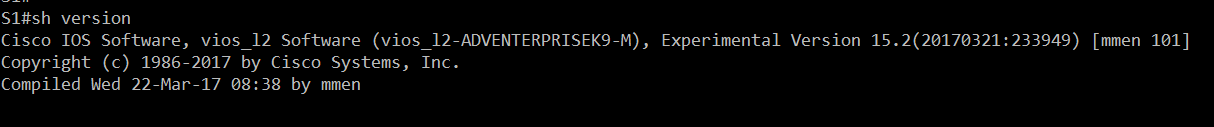
However, I observe that the commands are allowed but the protection mechanism does not take effect. I have no debug messages in the console .
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [February 16, 2023, 7:04am UTC](https://forum.networklessons.com/t/ipv6-dhcpv6-guard/3705/13 "2023-02-16T07:04:55Z")
Hello José
So you’re able to implement all of the commands in your IOS version. Indeed the version number seems to support DHCPv6 security features, including DHCPv6 Guard. Now in your particular case, you are not seeing the same debug messages as in the lesson? Well, first ensure that you’ve enabled the correct set of debugging like so:
```auto
SW1#debug ipv6 snooping dhcp-guard
IPv6 snooping - DHCP Guard debugging is on
```
Secondly, compare your output with that of the lesson when you issue the `show ipv6 dhcp guard policy` command and ensure that it is indeed enabled correctly.
If you’re still having problems, please give us some more information about your particular configuration and topology so that we can help you troubleshoot further.
I hope this has been helpful!
Laz