# OSPF TTL Security Check
**URL:** https://forum.networklessons.com/t/ospf-ttl-security-check/1941
**Category:** Lessons Discussion
**Created:** [July 19, 2017, 2:29pm UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941 "2017-07-19T14:29:02Z")
**Posts on this page:** 16
**Page:** 1
### Author:  [@ReneMolenaar](https://forum.networklessons.com/u/ReneMolenaar)
#### Post date: [July 19, 2017, 2:29pm UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/1 "2017-07-19T14:29:02Z")
This topic is to discuss the following lesson:
> **[OSPF TTL Security Check](https://networklessons.com/ospf/ospf-ttl-security-check)**
>
> The OSPF TTL security check sets the TTL of OSPF packets to 255 and only accepts packets with the configured TTL threshold
---
### Author:  [@chrisnewnham17](https://forum.networklessons.com/u/chrisnewnham17)
#### Post date: [October 11, 2017, 10:43am UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/2 "2017-10-11T10:43:46Z")
I guess if the person spoofing is capable of spoofing a TTL of 2, they are also capable of spooing a TTL of 256 which (with the default config) would effectively override this safety mechanism in this scenario 🙂
Unless the TTL is an 8 bit field, so 255 is the highest value!
---
### Author:  [@chrisnewnham17](https://forum.networklessons.com/u/chrisnewnham17)
#### Post date: [October 11, 2017, 11:06am UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/3 "2017-10-11T11:06:56Z")
Also you said this:
> [@](#):
>
> By default, the lowest TTL that OSPF TTL security check will accept is 255. You can add the hops parameter to use another value. For example, if you use ttl-security all-interfaces hops 100 then OSPF will accept all OSPF packets with a TTL of 155-255.
might be a change for IOS 15, but now the hops value is the maximum hop value, not the decrement amount.
[quote]ttl-security all-interfaces hops ?
\<1-254\> maximum number of hops allowed[/quote]
So if you wanted a TTL of 155 you would use the number 155, not the number 100
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [October 16, 2017, 2:06pm UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/4 "2017-10-16T14:06:02Z")
Hello Chris
Yes, you are correct that the TTL field is an 8 bit field, so the highest value can be 255.
I hope this has been helpful!
Laz
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [October 16, 2017, 2:23pm UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/5 "2017-10-16T14:23:07Z")
Hello again Chris.
You must remember that the value configured in the `ttl-security all-interfaces hops` command is the number of **allowed hops** and not the actual value of the TTL field. The value is essentially a threshold.
The default value is actually 0. This means that it will accept any values of TTL equal to or greater than 255-0. Since routing decrements the TTL by one, this means that only OSPF packets from directly connected devices will be accepted.
If this threshold is configured at 100 hops, then only packets with a TTL higher than 255-100 = 155 will be accepted. That means that packets with a TTL within the range of 155 to the maximum of 255 will be accepted.
I hope this has been helpful!
Laz
---
### Author:  [@arindom.nag](https://forum.networklessons.com/u/arindom.nag)
#### Post date: [April 25, 2018, 8:16am UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/6 "2018-04-25T08:16:33Z")
Hi Rene,
Hopefully you are doing good..
I have one question When i am going through you CCIE R&S Written Table of Contents here why **3.6e:Path Preference & 3.6f:Operations** not showing anything when i am trying to click there no page is opening so are you want to add any content there or its mistake by you? then 3.6g:Convergence and Scalability having content because when i clicking the + button the content is coming.
For your reference i attached the screenshot as well.
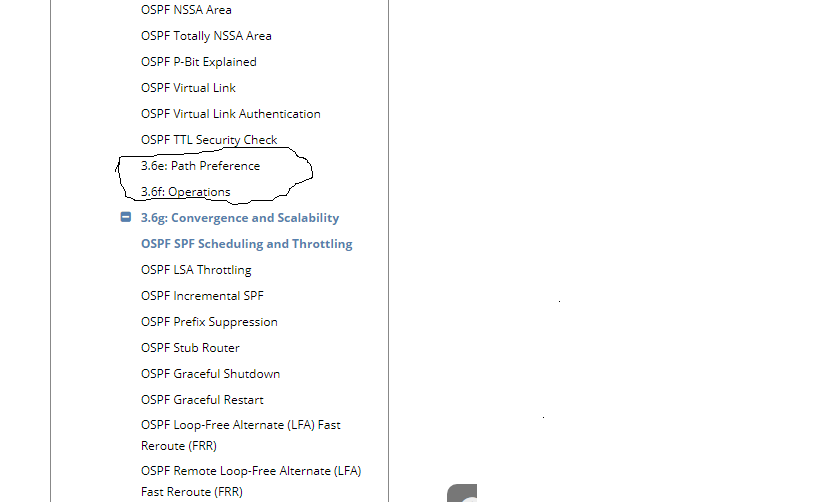
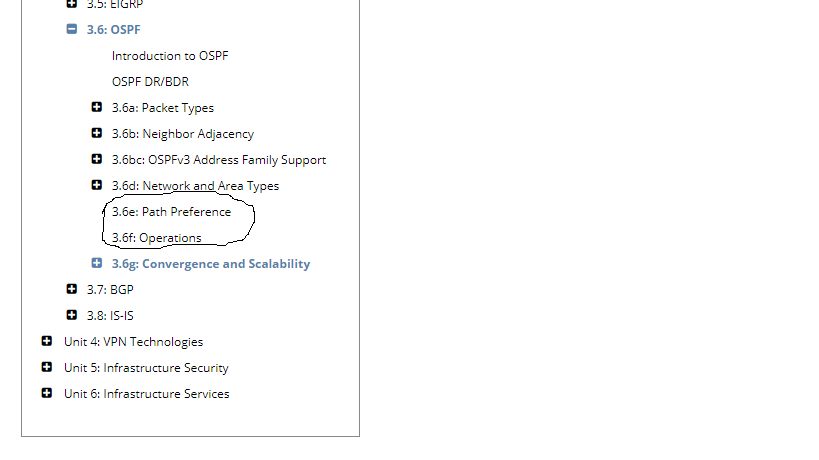
Thanks & Regards,
Arindom
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [April 30, 2018, 11:31am UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/7 "2018-04-30T11:31:30Z")
Hello Arindom
Thanks for that! I have sent out a message to Rene to take a look and fix it!
Laz
---
### Author:  [@ReneMolenaar](https://forum.networklessons.com/u/ReneMolenaar)
#### Post date: [May 1, 2018, 7:01am UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/8 "2018-05-01T07:01:00Z")
Hi Arindom,
I just moved a couple of items of 3.6f that should be there but weren’t.
3.6e is empty right now so that is a bit confusing. I’ll have to check which items can go there.
Rene
---
### Author:  [@arindom.nag](https://forum.networklessons.com/u/arindom.nag)
#### Post date: [May 4, 2018, 4:44pm UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/9 "2018-05-04T16:44:49Z")
Hi Rene,
Thanks for replying … if you add any thing there defenately I will go through the point..
Thanks & Regards,
Arindom
---
### Author:  [@gowthamraj4](https://forum.networklessons.com/u/gowthamraj4)
#### Post date: [November 15, 2020, 1:18pm UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/10 "2020-11-15T13:18:30Z")
Hi Rene,
FYI
As per your lesson
```
R1(config)#router ospf 1
R1(config-router)#ttl all-interfaces
```
i can see the syntax as 
i don’t know is typo error or older IOS version syntax will be this
i am using 7200 series router with IOS 15.0
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [November 16, 2020, 10:56am UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/11 "2020-11-16T10:56:48Z")
Hello Gowthamraj
Yes, you are correct, the command is indeed `ttl-security all-interfaces`. I was unable to find the syntax described in the lesson so I assume that this is a typo. I will let Rene know to confirm and make the modification as needed.
Thanks for pointing that out!
Laz
---
### Author:  [@ReneMolenaar](https://forum.networklessons.com/u/ReneMolenaar)
#### Post date: [November 16, 2020, 11:32am UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/12 "2020-11-16T11:32:43Z")
Hi @gowthamraj4
Thank you. I agree with @lagapidis, this is probably a typo. I just fixed it.
Rene
---
### Author:  [@joseph](https://forum.networklessons.com/u/joseph)
#### Post date: [December 9, 2020, 1:50pm UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/13 "2020-12-09T13:50:05Z")
Hey guys,
Do you have any lesson on TTL Security Check for eBGP?
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [December 11, 2020, 5:51am UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/14 "2020-12-11T05:51:13Z")
Hello Joseph
There’s currently no lesson on TTL Security Check for BGP, however, you can take a look at this post which talks a little bit about it, and also links to relevant Cisco documentation.
> [@EBGP Multihop](https://forum.networklessons.com/t/ebgp-multihop/1228/97):
>
> Hello Varun First off, it is not common practice to create a multihop scenario between routers that are so far away. In essence, the number of hops can change at any moment, and will actually be different depending on the path taken between the two routers. In general, it’s a good idea to avoid multihop whenever possible on the Internet. It’s more of a design issue rather than an issue of technical capabilities. Having said that, it is always possible to set the multihop to a high enough va…
If you’re interested, you can make a suggestion to add a lesson on the topic at the Member Ideas page below:
> **[Lesson Ideas - NetworkLessons.com](https://networklessons.com/lesson-ideas)**
>
> This page allows networklessons members to share what content they would like to see in the future.
I hope this has been helpful!
Laz
---
### Author:  [@narad](https://forum.networklessons.com/u/narad)
#### Post date: [July 4, 2021, 4:59pm UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/15 "2021-07-04T16:59:53Z")
@lagapidis
The moral of the story is , if i configure the TTL vale as 10 it means the Maximum Hops allowed between 11-255(255-10=245)..Right ??.
Then , Rene configured the TTL value as 255 it means (255-255=0). So it will accept only directly connected .
Lets say i have 3 router (R1–\>R2–\>R3), R3 is the attacker and i have configured the TTL security in R1and R2 as 255 , Now the question is , What will happen when R3 as an attacker will send the unicast packet R1 as TTL 30 ??..How R2 will prevent the attack before it reaches to R1 , can u explain little bit please..!
---
### Author:  [@lagapidis](https://forum.networklessons.com/u/lagapidis)
#### Post date: [July 31, 2021, 5:35am UTC](https://forum.networklessons.com/t/ospf-ttl-security-check/1941/16 "2021-07-31T05:35:54Z")
Hello Narad
Yes, theoretically speaking, if you configure the following:
`ttl-security all-interfaces hops 10`
then your OSPF router will accept any OSPF packets with a TTL greater than or equal to 10, but will reject all OSPF packets with a TTL of 9 or smaller.
Keep in mind that OSPF adjacencies **always take place between directly connected devices**. There should never be a router (or attacker) that is more than one hop away that can potentially become a neighbor. To be honest, I’m not sure why this command allows you to adjust the number of hops. The only reason I can think of is that you may have OSPF devices (of other vendors?) that may not be able to send OSPF packets with a TTL of 255 but may be able to be configured to do so with a smaller TTL. In any case, by using a TTL smaller than 255, you are negating the benefits of the feature, and opening a security hole. I believe best practice would be not to adjust the TTL and let it remain at 255.
Now for the scenario that you describe, in actuality, it is not R2 that will prevent the attack, but it is R1 that will simply not accept the OSPF packet because it has a TTL of 30 and not a TTL of 255.
I hope this has been helpful!
Laz