Hello Rahul
Thanks for pointing that out! I will let Rene know to make the changes…
Laz
Hello Rahul
Thanks for pointing that out! I will let Rene know to make the changes…
Laz
Thanks @Rahul_K I just fixed this.
Rene
Hello Rene, this line still has wrong Router Hostname. It should be Spoke2 and not Spoke1 since the configuration being done is for Spoke2.
Thanks again @Rahul_K . I fixed this one as well.
Rene
Hello Rene,
I have used your template for dual hub single but the issue is that when i do the trace my spoke site goes to hub 1 then hub 2 then hub 1 again and then to local network. on Hub 2 i configured nhs and nhrp so that hub 2 is considered as a client of hub 1. How can i solve this issue. Any idea
Hello Salman
If you take a look at the routing table of your spoke, you will find that you have two equal cost paths to both hubs. You should see something similar to this:
Spoke1#show ip route ospf

      1.0.0.0/32 is subnetted, 1 subnets
O IA     1.1.1.1 [110/1002] via 172.16.1.2, 00:01:50, Tunnel0
                 [110/1002] via 172.16.1.1, 00:05:01, Tunnel0
      4.0.0.0/32 is subnetted, 1 subnets
O        4.4.4.4 [110/1001] via 172.16.1.4, 00:04:51, Tunnel0
O IA  10.10.10.0/24 [110/1001] via 172.16.1.2, 00:01:50, Tunnel0
                     [110/1001] via 172.16.1.1, 00:05:01, Tunnel0
Note that 1.1.1.1 has two equal-cost paths via 172.16.1.1 and 176.16.1.2, the two hubs. When this occurs, you will find that OSPF will attempt to load balance traffic between equal-cost routes, and it will do this by alternating between the two available routes. This is why you see the behavior you are describing.
Now there are a couple of solutions that you can use to resolve this: use a distribute-list or use summarization. Neither is ideal as stated and explained in the lesson.
As stated at the very end of the lesson:
As we have seen, adding a second hub using a single cloud is very easy to configure but routing can be challenging. Since we use a single multipoint GRE interface, it’s difficult to prefer one hub router over another. Because of this, it’s unlikely to see this setup in production.
It is always preferable to use the dual hub dual cloud solution if you want to introduce redundancy at the hub.
I hope this has been helpful!
Laz
Hi,
I have to configure 3 HUBS. In this case I think only the 1st HUB has to be configured on 2nd and 3rd. But will OSPF work if HUB1 stops? Do I need to configure both the H1 and H2 on H3? And H1, H2 to each other?
Hello Barnabas
Yes, it is possible to have three or more hubs in a DMVPN configuration. You simply have to create a third hub in the same way you created the first and second hubs, and then on the spokes make sure to add an additional NHRP map command. You can find more information on how to do this in the following two Cisco community posts:
I hope this has been helpful!
Laz
Hi,
In my case two Hubs in one site and they are connected on LAN with EIGRP routing so I think I don’t have to create DMVPN tunnel between them, but the 3rd Hub is on another site. In this case I think I must create two static tunnels from the 3rd Hub to the first two, must not I?
Hello Barnabas
If you are configuring a single cloud scenario, then yes, you will need there to be a link between the primary hub and both secondary hubs. The two secondary hubs act as “clients” of the primary hub and require a connection. However, you only need to create a link between each secondary hub and the primary hub.
Now if you’re implementing the dual cloud scenario, you won’t need to explicitly create a tunnel between the hubs like you do in the previous scenario, because in this case, the secondary hubs are not clients of the primary hub. Each hub is configured independently.
I hope this has been helpful!
Laz
Hello Rene/Laz,
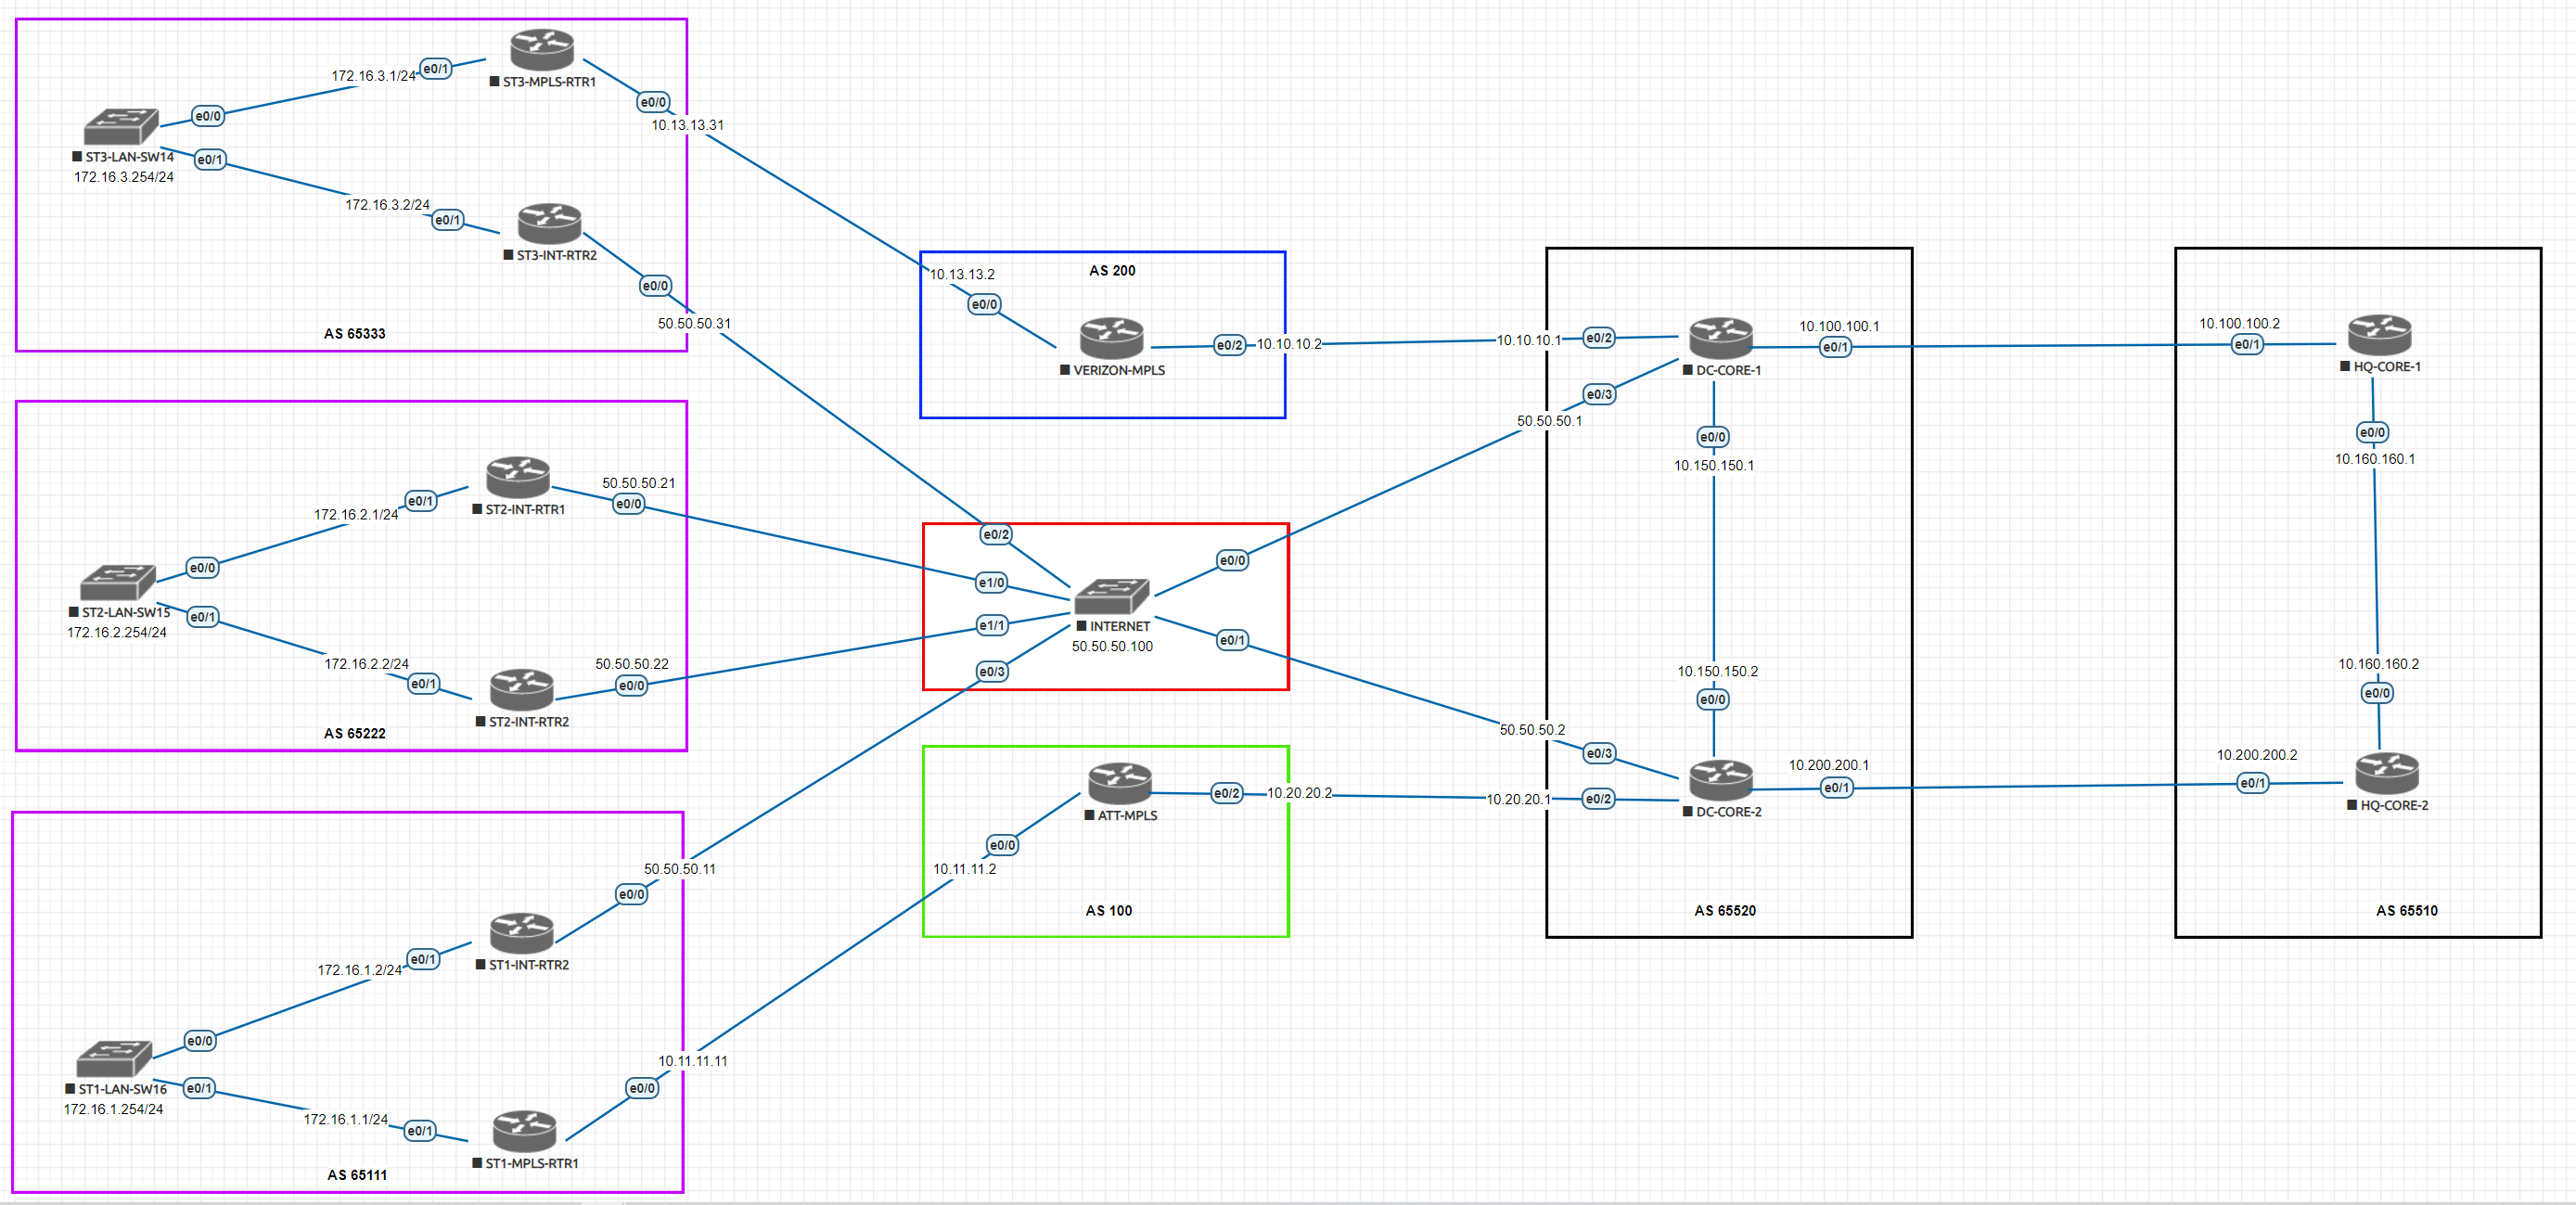
I am referring to the below diagram for my question. The topology has one DMVPN cloud with two Hubs: DC-CORE-1 and DC-CORE-2. However, the MPLS connection is being used as the primary connection here, but Site 2 does not have any MPLS circuit. Instead site 2 has two internet connections. In this setup, MPLS is preferred to be the primary circuit whenever available. No ECMP is not expected in this setup and full symmetric routing is desired. What would be the best approach to design this in terms of routing protocols. In another words, what routing protocols should be used here? Please provide me a high level configuration example if possible.
Thanks a lot.
Hello Azm
First, you should ensure that your underlying DMVPN dual hub single cloud setup is correctly configured. In your scenario, you have redundant links at the spokes, and since we are using a single mGRE tunnel, you must create a single tunnel interface on each spoke that uses a loopback interface as the source tunnel.
Once that is done, in order to ensure the proper redundancy, you will have to ensure that the loopack address is reachable via the routing protocol you use. From there on, you simply have to employ a routing protocol that will correctly route traffic as you desire. OSPF may not be the best choice because of the fact that you want to prefer the MPLS networks over the Internet. As demonstrated in the lesson itself, it’s difficult to use OSPF to prefer one hub over another.
EIGRP may be a better option as it gives you more flexibility in preferring one hub or path over another. Ultimately, the best way f examining the behavior of such a topology is to test it out in a lab scenario. If you do so, keep us posted as to your progress…
I hope this has been helpful!
Laz
Hi,
Could you not just use the area range with the cost option and a higher value? That way you can still advertise the un-summarised network into Area 1 but the Type-3 LSA generated by the Hub 2 ABR will have a higher metric than Hub 1 ABR.
Or couldn’t you just increase the cost on Hub 2 Gi0/3 to be higher than Hub 1 Gi0/3?
Regards,
Sam
Hello Sam
Yes, that is an option as well. You can have more granular control over the “summarization” method that Rene mentions in the lesson by adjusting the cost of the summarization in the area range command. It’s still a bit inelegant, but it works! Thanks for the suggestion!
Of course, this assumes that your IP addressing scheme allows for summarization to occur, without interfering with routes that may exist on your network that fall within the summarization range.
I hope this has been helpful!
Laz
Hi Laz,
I used phase 3 and point-to-multipoint on tunnel interfaces as a lab practice with single cloud.
Area 1 was configured as a totally stubby area and the default route cost and tunnel interface costs were modified on the hubs to ensure traffic to/from R1 and Spokes was via Hub1.
Redirects built spoke to spoke tunnels when necessary.
Is there any reason why this approach cannot also be used as a solution for a single cloud scenario?
Thanks.
Sam
Hello Sam
Yes, your approach is absolutely valid and can be used as a solution for a dual hub single cloud scenario. Your configuration using DMVPN Phase 3 with point-to-multipoint OSPF, totally stubby area configuration, and cost tuning is a recognized best practice design for DMVPN dual hub deployments.
I hope this has been helpful!
Laz
If the dual hub single cloud setup is configured as DMVPN phase 3, and the secondary hub is configured as a spoke to the primary hub, as in the example, what are the thoughts on the “ip nhrp shortcut” command on the secondary hub?
As I understand the purpose of the command, it allows for the shortcut routes to be installed when advertised from the (primary) hub, but as the secondary hub already should have routes to all spokes, as the spokes are set up to use both hubs, and the secondary hub is also set up as a spoke to the primary hub, it “ip nhrp shortcut” actually (technically) needed on the secondary hub?
My thoughts are that the command is not necessary, but still, as the command is a default, I have not found any configuration examples where the command is removed. So, either I am missing something or the command just does not break anything even if not needed and is therefore left in place…?
Hello Jacob,
I think your understanding is correct. In a dual-hub, single-cloud DMVPN Phase 3 design, ip nhrp shortcut is not strictly required on the secondary hub provided that all spokes register with both hubs and the secondary hub already has normal routing/NHRP reachability to all spoke networks.
The main purpose of ip nhrp shortcut is on a router acting as a Phase 3 spoke: it allows the router to accept/use NHRP redirect information from a hub and install/use shortcut forwarding toward the real destination. In the usual Phase 3 model, hubs use ip nhrp redirect, while spokes use ip nhrp shortcut.
Since the secondary hub is also functioning as a hub for the same cloud, and assuming it has registrations/mappings for the spokes directly, it does not need to learn shortcut paths from the primary hub in order to reach those same spokes.
That said, leaving the command in place is common and generally harmless. It also keeps the configuration consistent with Phase 3 templates and may be useful if the design later evolves into something more hierarchical, where the secondary hub may genuinely need to behave as a spoke toward another hub for certain destinations.
So I would summarize it this way: in the described topology, it is probably not functionally required, but leaving it configured is normal and usually not a problem.
Your discussion is very insightful and helps further understand the purpose of the command and the operation of DMVPN Dual Hub Single Cloud.
I hope this has been helpful!
Laz
Hi Laz,
Regarding @jacob’s question. I noticed that the ip nhrp shortcut command is on the tunnel interface by default and only visible when you issue the show run all command.
But in Phase 3 isn’t the OSPF (non-)Broadcast network type pointless for dual (and single) hubs as the next hop will always be the spoke’s tunnel IP anyway, and not the hub, as per point-to-multipoint, so an NHRP redirect will never be triggered by the hub? The spoke will simply query the NHS for the next hop overlay to NBMA address as it already knows it.
At least, that’s how I understand it.
Sam
Hello Sam
You raise an excellent, subtle point that touches the core of DMVPN Phase 3 design. To examine this behavior, we need to take a careful look at OSPF network types, next-hop behavior, and how NHRP redirect is actually triggered.
Remember the following:
Ultimately, however, your observation has merit, but it applies to Broadcast/Non-Broadcast network types. With OSPF broadcast/non-broadcast, the routing table may already point directly to the remote spoke’s tunnel IP, so the Phase 3 redirect/shortcut mechanism may not be exercised for those spoke-to-spoke routes. With other routing protocols, the dynamics may be different.
Now it is worth noting that OSPF can work, but it is often less attractive for large-scale Phase 3 designs because the main Phase 3 benefit is route summarization/default routing from the hub, and OSPF has limitations here, especially within a single area.The primary benefit of Phase 3 is the ability to advertise a summary or default route from the Hub to keep spoke routing tables small. OSPF does not allow intra-area route summarization, which limits this benefit. EIGRP or BGP are significantly more common and scalable choices for DMVPN Phase 3.
I hope this has been helpful!
Laz